
Hash functions play a significant function in cryptographic methods by making certain knowledge integrity. Even the slightest alteration to the enter generates a completely different hash, allowing customers to detect tampering successfully. Key management, or management of encryption keys, is the process of putting certain requirements in place to ensure the security of cryptographic keys in an organization.
Whereas HSMs have historically been deployed on-premises, migration to the cloud has also made HSMs available as a subscription-based service. Cloud-based HSMs ship dedicated hardware platforms as a service for purchasers to generate and handle keys without the necessity to buy and preserve their very own equipment. When moving functions and data to the cloud, organizations want to assume about how the level of possession, control and possession modifications to make sure a robust safety posture throughout the expanding computing ecosystem.
Cryptographic Keys Administration
- Given their important position, efficient management of SSH and PGP keys is important for an organization’s total safety and compliance posture.
- Every time an individual immediately handles a cryptographic key, the risk of error, theft, or misuse will increase.
- The crypto-period (i.e., lifetime) of static keys may range from days to weeks, months, or even years relying on what they are used for.
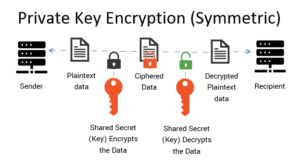
- Symmetric algorithms have the benefit in that they’re much sooner than asymmetric algorithms, and might deal with hundreds of keys with little or no computing overhead.
Key usage ensures the operational availability of keying materials in the course of the relevant crypto interval of the keys. Depending on the kind of key establishment protocols, the key could additionally be momentary (session key) and want revocation at the expiration finish of the digital certificates. Secure IP, hardware and software program to guard crucial data and techniques.
Key Management Finest Practices

Another issue to take into accounts for shielding keys is not solely access from external attackers, but also from insiders. The use of HSMs to guard and handle keys supplies mechanisms to establish twin controls, so no single inside individual or entity can change key use insurance policies and effectively subvert established security mechanisms. Quorum schemes the place a pre-determined minimum set of individuals should come collectively to affect any changes to the HSM and its key management https://tradeusanews.com/tesla-recalls-its-cars-due-to-software-and-security-problems.html capabilities additionally supplies enhanced levels of security. By implementing strong key management strategies and adhering to greatest practices, organizations can safeguard delicate data, stop unauthorized entry, and keep the integrity and authenticity of their data.
Also generally known as public-key cryptography, uneven encryption is a relatively newer encryption method that makes use of mathematically linked public and private key pairs to encrypt and decrypt information between trusted parties. Unlike symmetric encryption’s single key mannequin, uneven encryption makes use of paired keys (public and personal keys) for extra sturdy security. Subsequently, messages encrypted using a public key can solely be decrypted using a non-public key. Messages encrypted using a private key may be decrypted using a public key. They defend information at rest, secure communications in transit, authenticate users, and confirm the integrity of software and systems.
National School Transition Network (nctn ) – World Schooling
Only the person who is supposed to get the message and has the best personal key can read the message. Whereas the public key may be freely shared with anybody, the recipient should keep the personal key secret. Both are needed to decrypt the information and communications, and the non-public key can’t be mathematically derived from the basic public key, despite their linkage. For this purpose, uneven encryption is taken into account a extra sturdy and versatile strategy to encryption, regardless of being more computationally intensive. This mannequin underpins most blockchain techniques, digital wallets, and secure web communications.
A wallet’s public key (or derived address) identifies the place assets are held on a blockchain, while the non-public key grants the flexibility to authorize transactions. User-generated keys are inherently more advanced to implement because the finish consumer assumes one hundred pc ownership for random key era and safe key storage. These trade-offs are essential when knowledge must be accessible after a key purge. A user-generated key is the popular methodology when the top person has FIPS-certified algorithms.
